Shinra .OkoR991eGf.OhpWdBwm Ransomware Decryptor
Our cybersecurity division has developed a specialized decryption tool tailored for Proton/Shinra ransomware. This decryptor was created after in-depth reverse engineering of the encryption algorithms used by variants like .OkoR991eGf.OhpWdBwm. It has been extensively tested in enterprise environments, including Windows-based infrastructures and VMware ESXi, proving effective at restoring files without corruption or data loss.
How the Decryptor Operates
The Proton/Shinra decryptor leverages intelligence-driven mapping and secure execution protocols. By extracting the unique victim identifier embedded in ransom notes, it accurately aligns decryption keys with encrypted data.
For cases where the ransom note is missing, we offer a universal premium solution that uses simulated key models to rebuild lost keys. Before initiating the recovery, the tool runs a read-only system scan to confirm that encrypted files are recoverable, minimizing the risk of further damage.
System Requirements for Decryption
To achieve a successful file restoration, ensure the following prerequisites are available:
- A ransom note (commonly HELPME.txt or Recovery.txt)
- Access to encrypted files with the .OkoR991eGf.OhpWdBwm extension
- Administrative rights on the infected system
- Stable internet connectivity for secure key validation
Immediate Response After a Proton/Shinra Infection
Quick action is essential when dealing with this ransomware:
- Disconnect compromised systems immediately to prevent further spread.
- Do not delete ransom notes or alter encrypted files, as these are crucial for recovery.
- Shut down infected systems instead of rebooting to preserve volatile forensic data.
- Contact experienced recovery specialists before attempting self-directed fixes, which could lead to permanent data loss.
Free File Recovery Methods
While not always sufficient, certain free strategies may help victims recover data without paying a ransom:
Backup Restoration
If you have maintained offline or off-site backups, the safest route is to wipe infected systems and restore from clean backups. Always verify integrity before restoring to ensure no partial encryption occurred.
Snapshot Rollbacks
For virtualized setups like VMware, reverting to pre-attack snapshots may restore system functionality. However, always audit system logs first, as ransomware often attempts to delete snapshots.
Paid Recovery Options
When free recovery fails, victims may explore paid alternatives:
Paying the Attackers
While some victims consider paying the ransom, this comes with severe risks—including non-functional decryptors, hidden malware, or attackers withholding keys. Additionally, depending on jurisdiction, ransom payments may raise legal and ethical concerns.
Third-Party Negotiators
Professional negotiators may reduce ransom demands and confirm whether criminals provide valid keys. However, this approach is costly, time-consuming, and uncertain.
Enterprise-Grade Decryptor (Recommended)
Our proprietary decryptor is specifically designed to counter Proton/Shinra variants, including .OkoR991eGf.OhpWdBwm. It features:
- ID-based mapping to align keys with encrypted data sets
- Support for online and offline modes
- Sandboxed execution for safe decryption
- Blockchain-based verification to confirm integrity of restored files
Unlike attacker-supplied tools, ours ensures a secure and trustworthy recovery.
Step-by-Step Recovery Using the Proton/Shinra Decryptor
- Assess the Attack
Identify affected files and confirm the extension .OkoR991eGf.OhpWdBwm. - Secure Your Environment
Disconnect infected devices and confirm encryption scripts are no longer running. - Contact Our Recovery Experts
Submit a sample of encrypted files and the ransom note for analysis and confirmation. - Run the Decryptor
- Launch the tool with administrative privileges.
- Ensure internet access for secure server communication.
- Enter your victim ID from the ransom note for precise decryption.
- Start the tool and allow it to restore files safely.
- Launch the tool with administrative privileges.
About Proton/Shinra Ransomware
Proton/Shinra is a well-known ransomware family operating under the Ransomware-as-a-Service (RaaS) model. The variant .OkoR991eGf.OhpWdBwm is categorized as a V3 strain, where extensions are randomized strings, complicating detection and analysis.
Victims usually find ransom notes named HELPME.txt or Recovery.txt, with instructions to contact attackers via email and provide a unique victim ID.
Impact and Behavior of the .OkoR991eGf.OhpWdBwm Variant
This ransomware encrypts valuable enterprise data using hybrid cryptographic techniques, rendering files inaccessible. To hinder recovery, it removes Windows shadow copies and clears event logs using wevtutil.
Additionally, desktop wallpapers are often replaced with ransom messages, and Windows registry settings are modified to display forced legal notices.
Tools and Techniques Observed in Shinra Attacks
The Shinra group aggressively disables corporate environments by:
- Terminating processes tied to SQL databases, QuickBooks, VMware, and productivity tools
- Force-stopping antivirus and endpoint detection solutions
- Modifying registries, startup entries, and wallpapers to persist on systems
These tactics ensure seamless encryption and make recovery extremely difficult without specialized tools.
Indicators of Compromise (IOCs)
The following IOCs are linked to this strain:
- Extension: .OkoR991eGf.OhpWdBwm
- Ransom notes: HELPME.txt, Recovery.txt
- Attacker emails: [email protected], [email protected]
- Sample ID ransomware SHA-1: b0a3bdc32c006b4d2986115971b07d7be137fb1d
- Registry edits:
- Wallpaper set in HKCU\Control Panel\Desktop
- Legal notice added in HKLM\Software\Microsoft\Windows\CurrentVersion\Policies\System
- Wallpaper set in HKCU\Control Panel\Desktop
Sample hashes associated with related variants:
31eec61ed6866e0b4b3d6b26a3a7d65fed040df61062dd468a1f5be8cc709de7
d60d4624425b2f58dd9e37c40046f776e0d78cb031488a12c435239dd0da40ef
Tactics, Techniques, and Procedures (TTPs)
Proton/Shinra follows a highly targeted operational model:
- Initial access via stolen credentials, phishing, or exploitation of vulnerabilities
- Persistence through startup folder entries
- Defense evasion by disabling AV tools and deleting logs
- Impact through encryption, backup deletion, and ransom demands
- Exfiltration of sensitive data prior to encryption, increasing pressure with double extortion
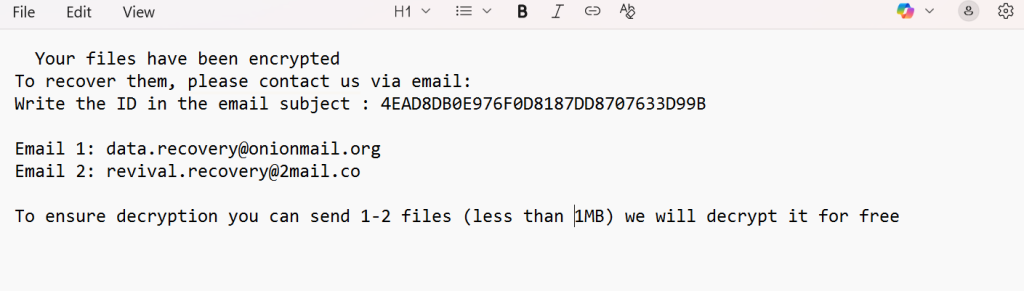
Example Ransom Note
A typical ransom note may read as follows:
Your files have been encrypted
To recover them, please contact us via email:
Write the ID in the email subject : 4EAD8DB0E976F0D8187DD8707633D99B
Email 1: [email protected]
Email 2: [email protected]
To ensure decryption you can send 1-2 files (less than 1MB) we will decrypt it for free
Victimology and Data Analysis
Shinra ransomware has targeted industries worldwide, with finance, healthcare, education, and managed service providers among the most frequent victims.
Key observations:
- Top countries affected: Global spread, with concentration in enterprise-heavy regions
- Industries hit hardest: Sectors with critical databases and virtualization usage
- Attack timeline: Often involves lateral movement before encryption to maximize disruption

Why Proton/Shinra Is a Major Threat
Unlike older strains that targeted single PCs, Proton/Shinra is engineered for network-wide disruptions. By combining randomized extensions like .OkoR991eGf.OhpWdBwm, advanced encryption, and data exfiltration, it poses a severe threat to modern enterprises.
Conclusion
Proton/Shinra ransomware is a formidable adversary due to its advanced encryption and destructive capabilities. Yet, with the right approach, data recovery is achievable.
Victims should:
- Contain the attack immediately
- Preserve all forensic evidence
- Explore both free recovery options and professional decryptors
Our decryptor has already enabled multiple organizations to restore their files without ransom payment, using both offline and cloud-assisted methods.
MedusaLocker Ransomware Versions We Decrypt