NoBackups Ransomware Decryptor
Our cybersecurity division has meticulously analyzed the encryption framework behind the NoBackups ransomware strain and engineered a dedicated decryption utility. This tool is purpose-built for recovering .nobackups files without paying threat actors. Designed for Windows environments, it offers rapid restoration, cryptographic integrity verification via blockchain, and guarantees zero file corruption.
This decryptor has already been deployed successfully across corporate enterprises, public sector institutions, and healthcare systems, demonstrating consistent accuracy and dependability.
Essential First Actions Following a NoBackups Breach
When ransomware strikes, every minute counts. Acting promptly can make the difference between a complete recovery and irreversible loss.
- Disconnect from All Networks — This prevents the ransomware from propagating to other systems or network drives.
- Retain All Evidence — Save ransom notes, encrypted samples, and relevant system logs for investigation and decryption purposes.
- Avoid Rebooting or Renaming — Changing file names may damage the encryption structure, making recovery more difficult.
- Consult Experts Immediately — Avoid unverified third-party tools, as they may be malicious or ineffective.
Free Recovery Avenues
If you maintain offline or secure cloud backups, the cleanest recovery route is to format the infected machine and restore verified copies. Always check the backups for integrity before restoration.
Should NoBackups fail to erase the system’s shadow copies, tools such as ShadowExplorer can be used to recover earlier file versions.
Currently, no legitimate free decryptor exists for .nobackups files. Be cautious — many fake tools circulate online, aiming to scam or reinfect victims.
Paid Recovery Possibilities
Not advised — there is no certainty the attackers will provide a functional key, and payments fuel further criminal activities.
Some specialized negotiators can potentially reduce ransom amounts but charge substantial fees and offer no guarantees of success.
How Our NoBackups Recovery System Functions
Our decryption methodology blends advanced reverse engineering with strict security measures:
- Victim ID–Linked Key Matching — The unique ID embedded in ransom notes is matched to encryption batches.
- Cloud-Sandbox Processing — Files are handled in a secured, isolated environment to ensure no additional compromise.
- Blockchain-Based File Verification — Confirms that decrypted files are authentic and untampered.
- Pre-Decryption Read-Only Scanning — Ensures data stability before the decryption process begins.
Step-by-Step Usage Guide for Our Decryptor
- Verify Infection — Look for .nobackups file extensions and the presence of README.TXT.
- Secure the Environment — Disconnect affected systems, restrict network connectivity, and secure your backup media.
- Submit Samples — Provide us with one ransom note and several encrypted files for analysis.
- Run the Decryptor — Execute with administrator privileges for maximum performance.
- Decryption Execution — Input your victim ID and let the tool restore original file states.
Understanding NoBackups Ransomware
NoBackups is a ransomware variant designed to encrypt user data, adding the .nobackups extension along with a victim-specific ID. Victims are presented with a ransom note (README.TXT) demanding payment under the threat of leaking stolen data within 24 hours.
Tactics, Techniques, and Procedures (TTPs) Employed by the Attackers
- Malicious email attachments containing macros or executable payloads.
- Exploiting outdated software and unpatched system vulnerabilities.
- Malvertising campaigns and fake application installers.
- A tailored encryptor appends .nobackups to targeted files.
- Utilizes hybrid AES (fast encryption) with RSA (key protection).
- Disables Windows recovery tools.
Deletes shadow copies using:
bash
CopyEdit
vssadmin delete shadows /all /quiet
- Extracts sensitive files before encryption.
- Implements “double extortion” by threatening to publish stolen data.
Utilities and Software Used by NoBackups Threat Actors
The NoBackups operation combines legitimate administration tools, well-known hacking utilities, and proprietary ransomware components. These are strategically deployed across different attack phases.
Credential Harvesting
- Mimikatz — Retrieves credentials stored in memory, browsers, and local stores.
- LaZagne — Dumps saved passwords from multiple applications.
Network Scanning and Mapping
- Advanced IP Scanner — Detects devices and services on the internal network.
- SoftPerfect Network Scanner — Identifies network shares and open resources.
Remote Access and Persistence
- AnyDesk — Allows covert, long-term remote control.
- Ngrok — Establishes secure tunnels to bypass network restrictions.
Data Exfiltration Tools
- FileZilla / WinSCP — Used for transferring stolen files to attacker-controlled infrastructure.
- RClone — Automates large data uploads to cloud platforms such as Mega.nz.
Encryption and Recovery Prevention
- Custom NoBackups Binary — Proprietary ransomware executable implementing AES + RSA encryption.
- vssadmin.exe — Eliminates Windows shadow copies.
- PowerShell Scripts — Disables antivirus, stops backup services, and removes recovery points.
Indicators of Compromise (IOCs)
- Encrypted File Extension: .nobackups
- Ransom Note: README.TXT
- Contact Email: [email protected]
- Session Messenger ID: Provided within ransom note
- Detection Signatures:
- Avast: Sf:WNCryLdr-A [Trj]
- ESET: Win32/Filecoder.WannaCryptor.D
- Microsoft: Ransom:Win32/WannaCrypt.H
- Avast: Sf:WNCryLdr-A [Trj]
Ransom Note Information
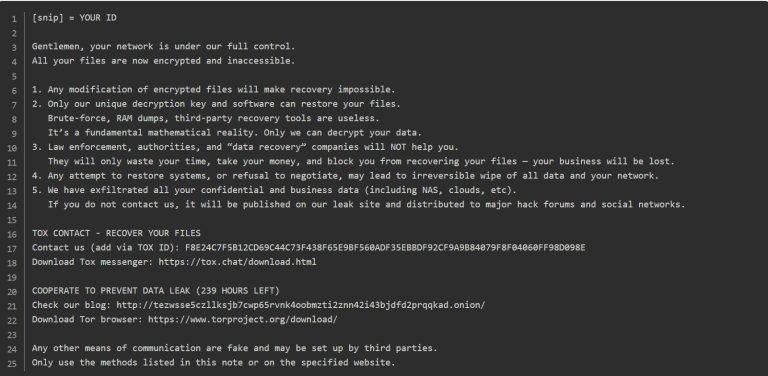
The ransom note (README.TXT) is dropped in every folder containing encrypted data. It directs victims to contact attackers through email or Session messenger, warns against renaming files, and offers decryption of one non-critical file as proof of capability.
Full Text of the Ransom Note:
YOUR FILES ARE ENCRYPTED
Your files, documents, photos, databases and other important files are encrypted.
You will not be able to decrypt it yourself! The only way to recover your files is to buy a unique private key.
Only we can give you this key and only we can recover your files.
To make sure that we have a decryptor and it works, you can send an email to: and decrypt one file for free.
But this file must not be of any value!
Do you really want to recover your files?
MAIL:[email protected]
Session:Download the (Session) messenger (https://getsession.org) You fined me: “0521cec653f519982a9af271f7ada8a41df1874549be9df509f6e8e0f2f53bb029”
Attention!
* Do not rename encrypted files.

Impact Analysis and Victim Statistics
Countries Affected

Industries Targeted

Attack Timeline

Preventive Measures Against NoBackups Attacks
- Enable multi-factor authentication for all remote logins.
- Keep operating systems and applications fully patched.
- Maintain multiple offline backup sets.
- Conduct regular security awareness training for employees.
Conclusion
While NoBackups ransomware is highly disruptive, it is not unbeatable. Using our specialized decryptor, victims can restore encrypted files without negotiating with cybercriminals, ensuring both security and control over the recovery process.
MedusaLocker Ransomware Versions We Decrypt