TheAnonymousGlobal Ransomware Decryptor
TheAnonymousGlobal Ransomware Decryptor: A Comprehensive Recovery Guide
TheAnonymousGlobal ransomware has emerged as one of the most insidious cyber threats in recent times. It infiltrates computer systems, encrypts critical data, and then demands a ransom in exchange for the decryption key. This guide explores TheAnonymousGlobal ransomware, its tactics, the damage it causes, and the best recovery methods, including an advanced decryptor tool designed specifically for this threat.
TheAnonymousGlobal Ransomware Decryptor: A Powerful Recovery Tool
The TheAnonymousGlobal Decryptor Tool has been developed to combat this ransomware effectively. It allows victims to regain access to their encrypted files without being forced to pay a ransom. Utilizing sophisticated decryption algorithms and secure online processing, this tool is a reliable and effective method for recovering data.
Key Features of TheAnonymousGlobal Decryptor
- Targeted Decryption
Specially designed to decrypt files that have been encrypted by TheAnonymousGlobal ransomware, including those with the .TheAnonymousGlobal extension. - Secure Recovery
The decryptor connects to secure servers to ensure data is recovered without compromising its integrity. - Easy-to-Use Interface
The tool is user-friendly and can be operated by individuals with varying levels of technical expertise. - Data Integrity Protection
It ensures that no files are deleted or damaged during the decryption process. - Guaranteed Results or Money-Back Assurance
If the decryptor fails to recover encrypted files, a refund is provided to ensure customer satisfaction.
TheAnonymousGlobal Ransomware’s Attack on VMware ESXi
TheAnonymousGlobal ransomware has been engineered to target VMware ESXi hypervisors, which play a vital role in many virtualized IT environments. Once inside, this malware can cripple virtual machines, halting critical business operations.
How It Targets VMware ESXi
- Exploiting Weaknesses in ESXi
The ransomware takes advantage of security flaws in ESXi hypervisors to gain access. - Robust Encryption Techniques
The malware employs AES and RSA encryption methods to lock virtual machine files, rendering them unusable. - Extortion and Threats
Attackers demand ransom payments in cryptocurrency, often threatening to permanently erase decryption keys if the ransom isn’t paid.
Consequences of an ESXi Ransomware Attack
- Severe Operational Downtime – Businesses relying on virtualized systems may experience prolonged outages.
- Significant Financial Losses – Organizations must bear costs associated with ransom demands, system recovery, and lost productivity.
- Potential Data Breaches – Attackers may steal confidential information from affected virtual machines.
TheAnonymousGlobal Ransomware’s Attack on Windows Servers
How It Infiltrates Windows Servers
TheAnonymousGlobal ransomware is also designed to target Windows-based servers, which house critical data and business applications. Given their importance, these systems are highly attractive to cybercriminals.
Attack Mechanism and Features
- Exploiting Security Vulnerabilities
Hackers leverage misconfigurations and software vulnerabilities to gain unauthorized access. - Encrypting Crucial Data
Using AES and RSA encryption, files on the infected server are locked, making them inaccessible. - Demanding Cryptocurrency Payments
Victims are pressured to pay ransom—often in Bitcoin—to receive the decryption key.
Impact on Businesses
- Loss of Sensitive Data – Without reliable backups, encrypted files may never be recovered.
- Disruption of Operations – Essential services and business activities may halt for extended periods.
- Damage to Reputation – Customers and partners may lose trust in a compromised organization.
How to Use TheAnonymousGlobal Decryptor Tool
Step-by-Step Guide to Recovery
- Securely Obtain the Tool
Contact us via WhatsApp or email to purchase the Decryptor and receive instant access. - Run as Administrator
Launch the tool with administrative privileges for smooth operation. A stable internet connection is required for it to connect with secure servers. - Input Your Victim ID
Locate your Victim ID in the ransom note and enter it into the tool to initiate the correct decryption process. - Start the Decryption Process
Begin decryption and allow the tool to restore files to their original state.
(Note: TheAnonymousGlobal Ransomware Decryptor requires a stable internet connection to function correctly.)
Signs of a TheAnonymousGlobal Ransomware Attack
Recognizing an infection early can help minimize damage. Key indicators include:
- Renamed or Modified Files – Files may have their extensions changed to .TheAnonymousGlobal.
- Ransom Note Appearance – A text file like “TheAnonymousGlobal_ReadMe.txt” appears, containing ransom demands.
Ransom note analysis:
Greetings.
All your files have been encrypted by TheAnonymousGlobal ransomware.
Please never try to recover your files without decryption key which I give you after pay.
They could be disappeared?
You should follow my words.
Pay $1000 BTC to below address.
My telegram : @TheAnonymousGlobal
Our Team : hxxps://t.me/Cyb3rDrag0nz_Team
We always welcome you and your payment.
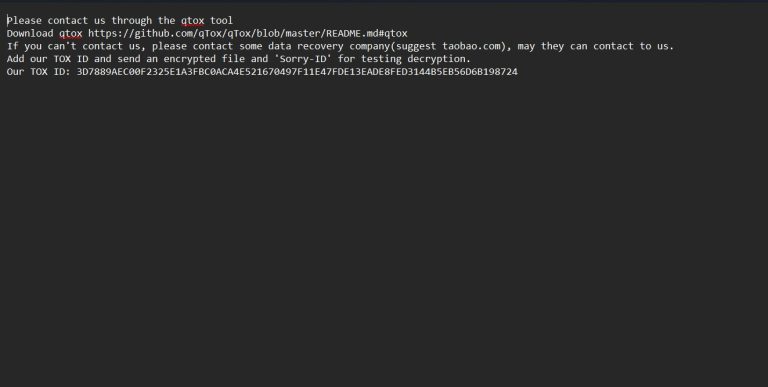
Screenshot of the ransom note:

The desktop wallpaper is also changed and the following text is displayed on it:
KILLNET
Your System Hacked By KillNet
Contact:@AnonymousGlobal
btc address:
bc1qpyg6tdmkc4cnatrp7nhu6mtmj4ejr232w97q2k
USDT Trc20 : TBzdndb3ahKaUCxXQ6LIsmtjKFsxY9tYVJF
- Performance Issues – High CPU and disk usage due to encryption activity.
- Unusual Network Traffic – Malware communicates with external command-and-control servers.
Who Has Been Affected by TheAnonymousGlobal Ransomware?
Organizations across various industries—including healthcare, finance, and government agencies—have fallen victim to TheAnonymousGlobal ransomware, facing severe disruptions and financial setbacks. These incidents underscore the need for robust cybersecurity measures and preventative strategies.
Encryption Techniques Used by TheAnonymousGlobal Ransomware
- RSA Encryption (Asymmetric Cryptography)
Uses public and private keys to lock files securely. - AES Encryption (Advanced Encryption Standard)
Ensures that files remain inaccessible without a unique key.
Best Practices for Ransomware Protection
1. Regularly Update and Patch Systems
- Apply security updates to operating systems, ESXi hypervisors, and critical applications.
- Stay updated with vendor security advisories.
2. Implement Strong Access Controls
- Enforce multi-factor authentication (MFA).
- Restrict user permissions and monitor access logs.
3. Network Segmentation for Security
- Isolate high-value systems and restrict unnecessary network connections.
- Use VLANs and firewalls to prevent lateral movement.
4. Maintain Secure Backups
- Follow the 3-2-1 backup rule (three copies, two storage formats, one offsite).
- Perform regular backup tests to ensure data recoverability.
5. Use Endpoint Security Solutions
- Deploy endpoint detection and response (EDR) tools to monitor for threats.
6. Conduct Cybersecurity Training
- Educate employees on phishing threats and ransomware prevention.
Stages of a Ransomware Attack
A ransomware attack typically follows this pattern:
- Initial Infiltration – Attackers gain entry through phishing, RDP exploits, or software vulnerabilities.
- File Encryption – AES/RSA encryption is used to lock files.
- Ransom Demand – Hackers demand cryptocurrency payments.
- Threat of Data Exposure – Attackers may leak sensitive files if payment isn’t made.
Consequences of a TheAnonymousGlobal Ransomware Attack
- Business Disruptions – Loss of access to data halts operations.
- Financial Strains – Beyond ransom payments, businesses face recovery and legal expenses.
- Reputation Damage – Data breaches can lead to customer distrust and legal penalties.
Alternative Recovery Methods
In addition to the TheAnonymousGlobal Decryptor Tool, consider these options:
- Use Free Decryptors – Check resources like NoMoreRansom.org for available tools.
- Restore from Backups – Recover data from secure, offline backups.
- Volume Shadow Copies – Retrieve previous versions of files if available.
- System Restore – Revert to an earlier system state.
- Data Recovery Software – Use tools like Recuva or PhotoRec to recover unencrypted remnants.
TheAnonymousGlobal ransomware is a highly destructive cyber threat. However, by implementing proactive cybersecurity measures, maintaining regular backups, and utilizing specialized tools like the TheAnonymousGlobal Ransomware Decryptor, victims can avoid ransom payments and recover their data efficiently. Strengthening security protocols today can prevent future attacks and safeguard critical information.
MedusaLocker Ransomware Versions We Decrypt